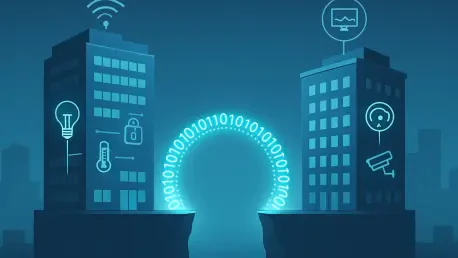
Operational technology teams often understand their specific platforms but remain unaware of how those systems interact with the broader corporate network. In the current landscape of 2026, the rapid integration of artificial intelligence and Internet of Things devices has transformed the modern office tower into a complex data center. While these innovations streamline operations and reduce carbon footprints, they also create a sprawling attack surface that traditional security measures struggle to cover. The primary hurdle for property owners is no longer the acquisition of high-tech tools but rather the creation of a management structure that keeps pace with them. Smart building ecosystems thrive on connectivity, yet this very connectivity serves as a bridge for malicious actors if not governed with precision. Real estate firms must recognize that the digital infrastructure of a building is just as critical as its physical foundation, requiring a unified strategy that encompasses every sensor and access control panel across the entire portfolio.
1. Reasons: Why Governance Structures Often Fail
The internal organizational structure of many commercial real estate firms remains tethered to outdated operational models that do not account for the convergence of digital and physical assets. Facilities management professionals are highly skilled at maintaining the physical integrity and mechanical efficiency of building systems, such as elevators and heating units, yet they frequently lack the specialized training needed to defend these systems against sophisticated cyber threats. Conversely, information technology departments are experts at securing servers and employee workstations but often have zero visibility into the operational technology networks that run the building itself. This fundamental disconnect creates a vacuum where critical security patches are missed, and unusual network traffic goes unnoticed because no single team possesses the complete picture. The resulting fragmentation means that a vulnerability in a basement cooling system could potentially provide a gateway for an attacker to move laterally into the main corporate environment.
Outside service providers and technology integrators further complicate the governance landscape by focusing solely on the performance of their proprietary installations. While a vendor may ensure that a new smart lighting system operates at peak efficiency, they rarely take responsibility for how that system integrates with the broader network architecture of the property. Many of these third-party platforms require remote access for maintenance, which creates permanent backdoors into the building infrastructure that the internal IT team may not even know exist. Without a centralized governance framework, there is no standardized protocol for vetting the security practices of these vendors or for monitoring their activities once they are connected to the network. This lack of oversight results in a mosaic of interconnected technologies where the weakest link is often a third-party sensor or a legacy controller that was never intended to be internet-facing. Consequently, accountability is shifted from one party to another, leaving the building owner with a high-risk asset.
2. Implementation: Pillars and Proactive Security Measures
To bridge these significant gaps, organizations must focus on three foundational pillars of effective cyber governance, starting with a comprehensive cataloging of all digital assets. This process involves identifying every piece of property and tenant data collected, tracing how information moves through the network, and pinpointing exactly where systems connect and vulnerabilities exist. Once visibility is established, the second pillar requires a rigorous assessment of protective measures through frequent risk evaluations and vulnerability testing against established industry frameworks. This ensures that the security controls in place are not just theoretical but are actually capable of repelling real-world attacks. Finally, the third pillar centers on continuous verification and reporting, using monitoring tools and third-party audits to provide leadership with clear, data-driven performance metrics. By formalizing these steps, firms can transition from a reactive security posture to one that is inherently strategic and measurable.
Building a resilient smart building strategy requires proactive leadership and the implementation of specific, high-impact actions designed to minimize risk. Leaders should prioritize the development of a detailed asset inventory that includes everything from IoT sensors to cloud services and vendor access points. This must be followed by a thorough risk evaluation of both IT and operational technology environments to align internal practices with recognized global security standards. A critical technical step involves implementing robust network segmentation, which isolates building automation devices from sensitive tenant networks and primary financial infrastructures to prevent cross-contamination during a breach. Additionally, defining clear accountability and ownership is essential for unifying facilities management and IT under a single decision-making process. Finally, organizations must prepare for potential disruptions by formulating and practicing incident response strategies specifically tailored to threats such as ransomware attacks or access-control failures.
3. FAQ: Why Is Smart Building Governance Essential?
The necessity of governance in smart buildings is driven by the expansion of an organization’s risk profile, as efficiency-boosting technologies also introduce new vulnerabilities. A governance framework connects these technical decisions to risk management and vendor oversight, ensuring that connected systems are adopted responsibly and securely. Governance often breaks down when information technology, facilities management, and vendor teams share responsibility without clear ownership. When each group manages only part of the environment, organizations lose visibility into connected systems, vendor access points, and data flows. This lack of coordination leads to portfolio-level vulnerabilities where no single party is accountable for the overall security posture. By establishing a unified structure, real estate leaders can bridge these departmental gaps and ensure that security standards are applied consistently across all properties. This holistic oversight is the only way to manage the complex interdependencies.
Securing a real estate portfolio begins with establishing complete visibility into the existing digital footprint of each property through a comprehensive inventory process. Leaders must first identify every connected device and sensor to understand the full scope of their exposure before they can proceed to assess risks and segment networks. Once the technical landscape is mapped, the focus shifts to establishing clear accountability protocols that bridge the gap between IT, facilities, and vendor teams. By defining who is responsible for each aspect of the system, leaders ensure that security patches are applied and that third-party access is strictly monitored. This foundational work allows for the creation of incident response plans that are tested before a disruption occurs, ensuring that the organization is ready to act decisively when a threat is detected. This comprehensive approach allows leaders to build a resilient infrastructure that protects both physical assets and corporate reputations in a digital age.
The organizations that successfully implement these governance strategies realize that resilience is a modern competitive advantage rather than just a technical necessity. By defining the attack surface early and collaborating with experienced advisors, these firms turn cybersecurity from a hurdle into a long-term strategic asset that protects property value and tenant trust. They move beyond the simple adoption of smart technology and instead focus on responsible innovation, ensuring that every new sensor or AI application is backed by a solid framework of accountability. This approach allows real estate leaders to satisfy the increasing security demands of institutional investors while maintaining the high operational efficiency that smart buildings promise. The most successful firms transition from viewing security as a cost center to treating it as a core pillar of operational excellence, which ultimately preserves their reputation in an increasingly connected market. By taking these actionable steps, they build a foundation of trust that becomes a distinguishing feature.